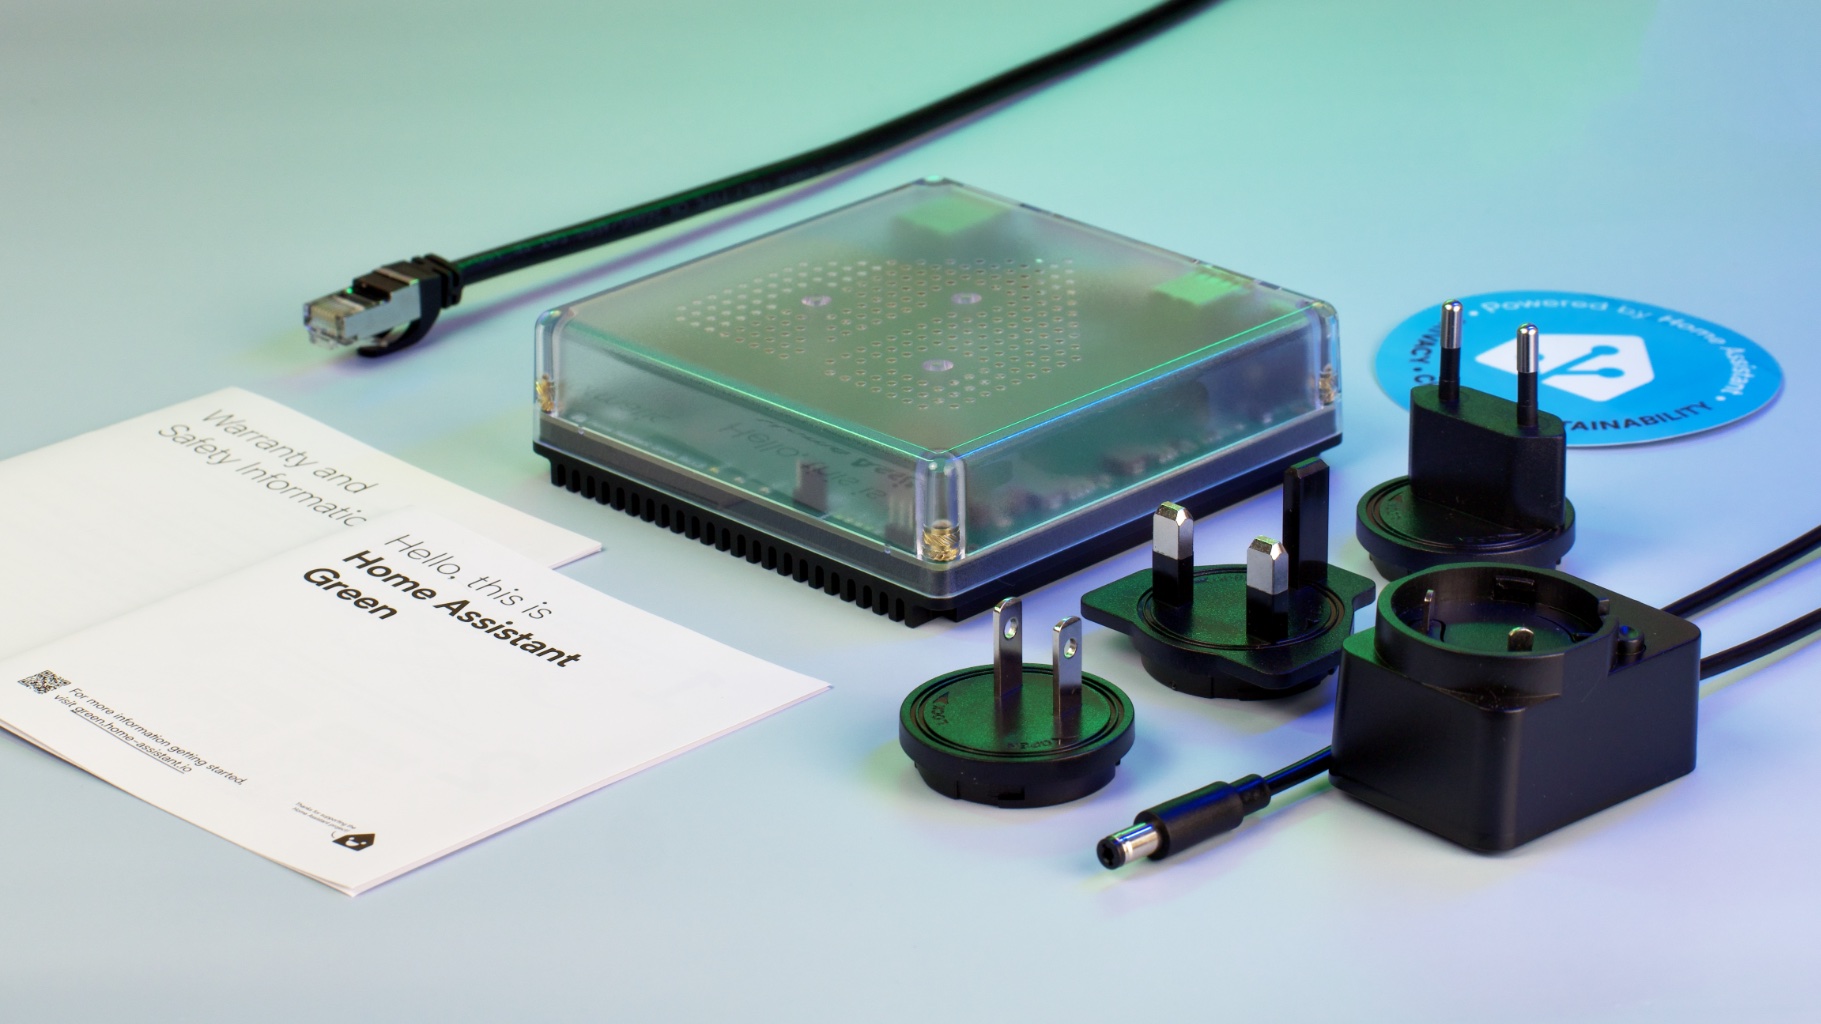
Home Assistant Green, a popular open-source home automation platform, was targeted at Pwn2Own Ireland 2025, resulting in a chain of vulnerabilities. I exploited an SSDP LOCATION SSRF to achieve unauthenticated remote code execution on the device. This vulnerability allowed the execution of commands by leveraging the go2rtc service.